AI-Powered CASB
Cloud Application Security Broker: iboss discovers every cloud and AI app in use, scores its risk, and controls what users can do inside each session, in the browser they already use.
From discovery to control.
How iboss finds every cloud app in use and applies DLP and in-app policy from one console.
Your app inventory is a guess.
File sharing, storage, messaging, AI: employees adopt whatever gets work done, and most of it never crosses an approval desk. Every uncataloged app is an unmonitored path for sensitive data.
iboss turns live traffic into a real inventory: every app in use, who uses it, what moves through it, and how risky it is.
Every app in use, found from live traffic.
No surveys and no self-reporting. iboss builds the discovered-app list from the traffic it already secures, including AI tools the moment they appear.
- +Automatic discovery across web, cloud, SaaS, and AI apps
- +Uploads, downloads, forms, logins, and users per app
- +Uncataloged queue that surfaces new apps for review
- +On-prem discovery for apps behind the firewall
| application | data risk | app risk | uploads |
|---|---|---|---|
| Google Drive | 50 | 10 | 1,734 |
| SendSpace | 80 | 60 | 593 |
| GitHub | 50 | 50 | 601 |
| WeTransfer | 80 | 50 | 1,206 |
| ChatGPTAI | 60 | 40 | 312 |
| OneDrive | 50 | 50 | 1,500 |
A researched profile for every app.
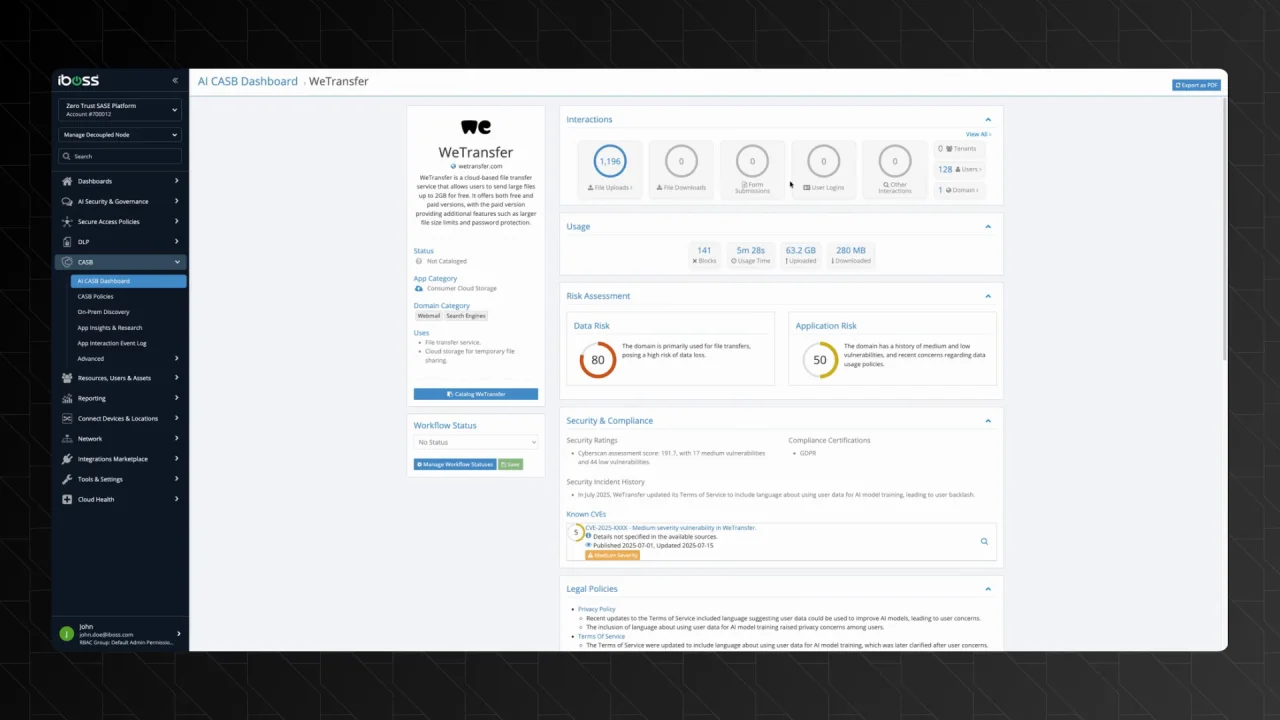
Each discovered app gets a continuously updated profile: what it does, how it handles data, and what has gone wrong before. Sanction decisions start from evidence instead of a domain name.
- +Data and application risk scores for every app
- +Known CVEs and security incident history
- +Legal and ToS analysis, including AI training clauses
- +Hosting, encryption, and compliance certifications
From shadow app to sanctioned tool.
Move each app through an explicit decision: approve it, monitor it, tolerate it, or shut it down. Tags drive policy, and every decision leaves an audit trail.
- +Catalog workflow with owners and review statuses
- +Tags from Approved to Unapproved, applied per app
- +Policy inherits the tag automatically across the platform
- +Complete decision history for audits
Sharing & Interacting
File Operations
Actions
Authentication
Form Controls
Commerce
Enterprise browser controls. Your browser.
Go past allow or block. iboss governs what happens inside each session: sharing, uploads, copy and paste, logins, forms, and purchases, enforced inline in any browser with nothing new to install.
- +Per-app control of sharing, files, clipboard, auth, and forms
- +Tenant restrictions keep people in corporate accounts
- +Identity-based: policies follow user, group, and risk
- +No browser replacement, works where people already work
Discovery feeds DLP. DLP protects everything.
CASB connects application visibility and control with iboss DLP and AI Security: one console, one policy engine, shared telemetry.
- +DLP inspects uploads and prompts across every discovered app
- +AI apps get the same discovery, scoring, and control
- +Single console for web, cloud, SaaS, and AI policy
See every app. Govern every session.
See how iboss CASB discovery and in-app control secure cloud and AI use across your organization.